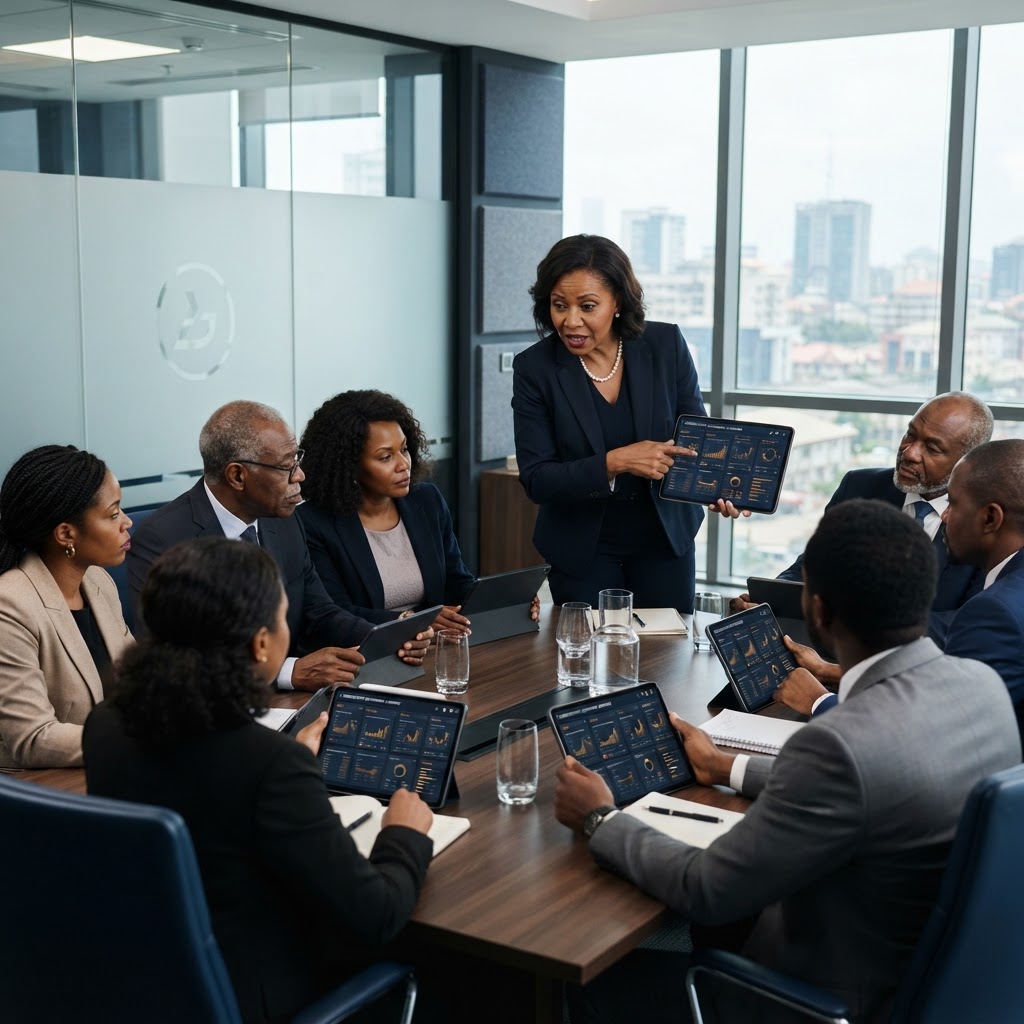
Board-Level Cyber Oversight: The New Mandate for African Directors
Cyber risk has moved from the server room to the boardroom. Across Nigeria and the wider continent, regulators, investors, and insurers now expect directors to demonstrate genuine oversight of technology risk, not delegate it blindly to IT.
Why Boards Must Own Cyber Risk
A board that cannot answer basic questions, such as what its most critical data assets are, or what the incident response plan looks like, is exposed on two fronts: operationally when an incident strikes, and legally when stakeholders ask what oversight was in place.
A Practical Oversight Framework
- Establish a risk appetite statement for technology risk, approved at board level and reviewed annually.
- Create a cyber dashboard with a small set of meaningful indicators, such as patching coverage, phishing simulation results, and backup restore test outcomes.
- Assign clear accountability, whether to a dedicated risk committee or an audit committee with an expanded mandate.
- Rehearse the response with an annual tabletop exercise that includes communications and legal response, not just technical recovery.
The African Context
Many African enterprises are digitising faster than they are formalising oversight. That gap is an opportunity: boards that build cyber governance now will find it easier to attract capital, pass regulatory scrutiny, and respond resiliently when incidents occur.
Sentinel GRC Partners works directly with boards to assess their cyber oversight maturity and implement pragmatic governance structures suited to the realities of the African market.